How to Set Up Homelab Network Segmentation: VLANs, IoT Isolation, and Firewall Rules
Learn how to set up homelab network segmentation with a practical five-zone VLAN model, IoT isolation, firewall rules, DNS, logging, and Proxmox and Docker placement guidance.
Disclosure: This article contains affiliate links. If you purchase through these links, HomelabAddiction may earn a commission at no additional cost to you.
Documentation basis: This guide is grounded in the OPNsense firewall and VLAN documentation, the Docker macvlan driver documentation, and vendor guidance for managed-switch VLAN tagging. The recommendations here are framed around documented behavior and supportable operational patterns rather than anecdotal shortcut stories.
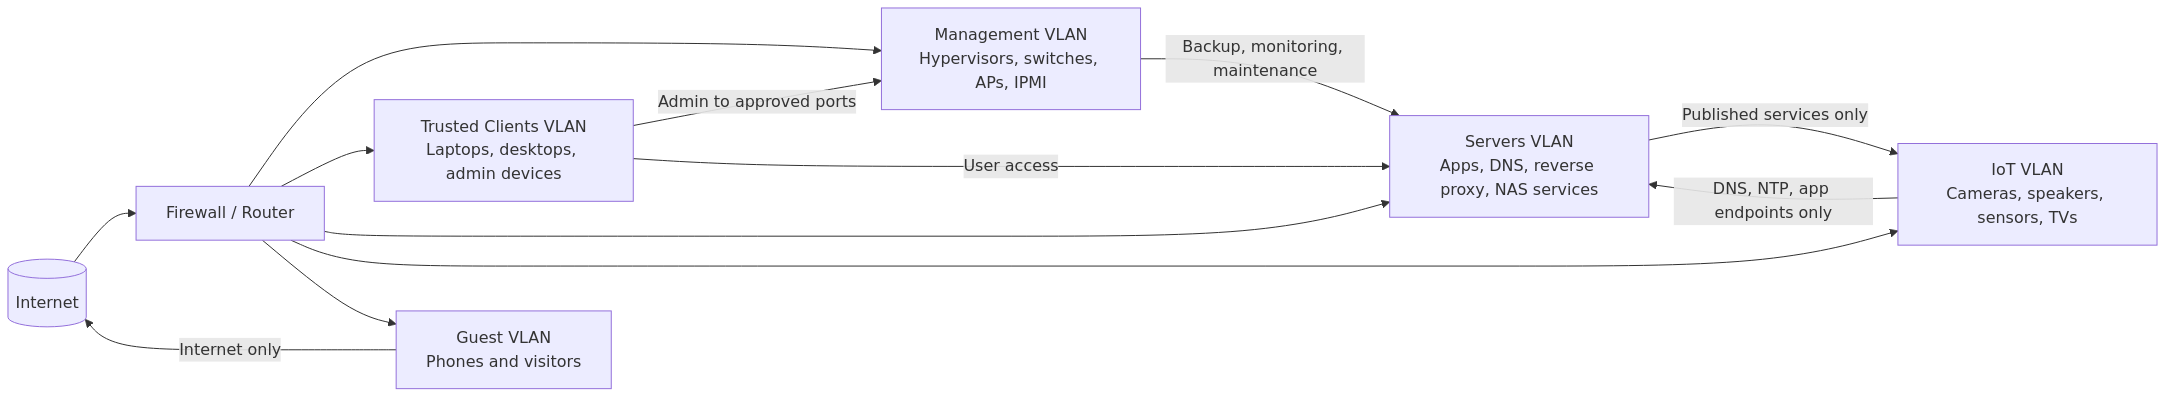
Homelab segmentation becomes easier to maintain when the design starts with a small number of zones that map to real jobs: administration, user devices, servers, IoT, and guests. That framing does more work than chasing large VLAN counts or copying enterprise diagrams that solve a different scale problem.
The main decision is not how many VLAN IDs to create first. It is which systems truly need to initiate traffic to each other, which services must cross boundaries, and where DNS, backup, and monitoring flows need explicit exceptions to stay predictable.
This walkthrough keeps the pattern grounded in documented firewall and VLAN behavior so a small lab can grow without turning policy cleanup into a recurring emergency.
Starter homelab segmentation layout: keep management, trusted clients, servers, IoT, and guests in separate zones, then allow only the flows each job truly needs.
Key Takeaways
Most homelabs only need five starter zones: management, trusted clients, servers, IoT, and guests.
Default-deny inter-VLAN rules stay workable when each allow rule names a specific service such as DNS, backups, monitoring, or reverse-proxy traffic.
DNS and logging are part of segmentation design, not optional cleanup after the VLANs already exist.
Add extra zones only when there is a clear risk or operational reason, not because the switch can technically host them.
What network segmentation is solving in a homelab
A flat network is comfortable right up until it is not. Your laptop, Home Assistant box, NAS, Proxmox host, test containers, cameras, printer, and whichever mystery device came with a cloud account you never asked for all share the same trust boundary.
That is convenient. It is also lazy.
Segmentation fixes three real problems:
1. Containment - if one device gets popped, it should not have line-of-sight to everything else.
2. Operational clarity - when traffic crosses a boundary, you can decide whether that should happen.
3. Troubleshooting - weird traffic is easier to understand when each network has a job.
The goal here is not enterprise cosplay. The goal is a layout that still makes sense when Docker services pull updates, backup jobs move data overnight, IoT devices chatter constantly, and someone has to troubleshoot the lab when they are tired.
Docker services pulling updates
Proxmox hosts moving backups
Home Assistant talking to IoT junk
reverse proxies reaching apps
guest devices staying out of everything that matters
Accepts connections from Trusted, limited outbound
IoT
10.10.40.0/24
Cameras, smart plugs, TVs, random Wi-Fi nonsense
Internet plus tightly scoped local exceptions
Guest
10.10.50.0/24
Visitors, temporary devices
Internet only
That is enough for most people.
If the lab grows beyond the starter pattern, add a sixth Lab network only when there is a clear isolation reason such as disposable testing VMs, risky container experiments, or temporary migration work.
Why separating management from server traffic reduces blast radius
Putting management interfaces on the same network as general server traffic increases the blast radius of ordinary mistakes. When a noisy container stack, misrouted host, or broad firewall test can also reach IPMI, switch, or hypervisor control planes, recovery gets harder right when you need it most.
transmission signup
article_topic // How to Set Up Homelab Network Segmentation
Don't leave without the setup notes.
Get practical homelab guides, failure logs, and beginner-friendly build notes in your inbox.
Enter your email address to receive the Homelab Addiction newsletter.
Weekly only. No spam. Unsubscribe anytime.
Separating management from server traffic limits which systems can reach the control plane, makes lockout scenarios easier to reason about, and gives firewall policy a clearer job description.
The access model before the firewall rules
Do not start by writing rules. Start by answering who should initiate connections.
That usually looks like this:
Trusted -> Management: allowed for HTTPS, SSH, and whatever your switches/APs need
Servers -> Internet: allowed for updates, package repos, DNS, NTP
IoT -> Internet: allowed, but keep it narrow where possible
IoT -> Servers: blocked by default, with exceptions only if something genuinely needs local control
Guest -> Anything internal: blocked
Management -> Everything: usually limited to administration and monitoring, not casual browsing
If you already have a good mental model for firewall policy, the companion guide on homelab firewall rules pairs well with this segmentation walkthrough.
A sane firewall matrix
Here is the boring but useful version.
Source
Destination
Allow?
Typical ports / notes
Trusted
Management
Yes
443, 22, vendor management ports
Trusted
Servers
Yes
80, 443, 22, 2049, 445, app-specific ports
Trusted
IoT
Sometimes
Home Assistant control, printer access, cast targets
Servers
Internet
Yes
80, 443, 53, 123
Servers
Management
Rarely
Monitoring or backup hooks only
IoT
Internet
Yes
Usually 80, 443, NTP, DNS
IoT
Servers
No by default
Add narrow exceptions if required
IoT
Trusted
No
This should stay blocked
Guest
Internet
Yes
NAT out, no internal access
Guest
RFC1918 networks
No
Block 10/8, 172.16/12, 192.168/16
The pattern is simple:
allow known flows
block sideways movement
log denied traffic during rollout
That last part matters. Traffic logs are where you discover that your TV wants to discover a media server across VLANs, your backup job was hardcoded to an IP you forgot about, and one app treats DNS failure like a personal insult.
VLAN design for Proxmox, Docker, and storage
This is where generic home-network articles usually go soft. A homelab is not just laptops plus a guest SSID. You are probably running a hypervisor, containers, maybe storage, maybe monitoring, maybe all of them on a box you promised yourself was temporary in 2024.
A practical default placement looks like this:
Proxmox management UI on Management
Proxmox VM and container workloads on Servers or Lab, depending on risk
NAS and backup targets on Servers
Reverse proxy on Servers
Monitoring stack on Servers
Home Assistant either on Servers or a dedicated automation VLAN if you are unusually committed to pain
For Proxmox networking details, read Proxmox Networking Explained. The short version is that VLAN-aware bridging keeps life manageable.
That puts the host management interface on VLAN 10 while allowing tagged VM traffic across the bridge.
Example Linux VLAN interface
If you need a tagged interface on a Linux box:
ip link add link eno1 name eno1.30 type vlan id 30\nip addr add 10.10.30.25/24 dev eno1.30\nip link set eno1.30 up
ip link add link eno1 name eno1.30 type vlan id 30
ip addr add 10.10.30.25/24 dev eno1.30
ip link set eno1.30 up
Simple, explicit VLAN interface definitions are usually easier to audit and recover than clever but undocumented shortcuts.
Docker changes the conversation
Docker is convenient, but segmentation gets awkward if you pretend every container is a first-class network citizen. Most of them do not need to be.
A practical baseline rule is simple:
keep most app containers behind a reverse proxy on the Servers network
do not throw containers directly onto separate VLANs unless you have a clear reason
reserve special networking modes for services that truly need layer 2 presence or multicast weirdness
The official Docker docs on macvlan networking are worth reading before you get adventurous. Macvlan looks elegant until you discover host-to-container communication caveats and start inventing side interfaces to compensate.
A normal Compose stack for internal services usually belongs on one server VLAN behind an ingress layer:
That design keeps east-west app traffic internal while exposing only the proxy entrypoint.
DNS is where segmentation either works or becomes a hobby
Most segmentation writeups treat DNS like a side note. That is adorable.
DNS is the reason people think segmentation broke the network, when what actually broke was name resolution, service discovery, or a bad assumption about how clients find services.
A supportable DNS pattern for small homelabs looks like this:
run one local resolver stack on the Servers network
allow DNS from Trusted, Servers, and IoT to that resolver
use local records for internal services
use split-horizon DNS if the same service name must resolve differently inside and outside the lab
For resolver options, compare Pi-hole vs AdGuard Home by the client controls, DNS features, and maintenance style the lab actually needs. The main point here is centralizing DNS, not attaching identity to one resolver stack.
Why split-horizon DNS matters
Suppose grafana.example.net points to your public reverse proxy externally, but internally you want that name to resolve to 10.10.30.15.
Without split-horizon DNS, you often end up with one of these bad outcomes:
internal clients hairpin through the public endpoint
TLS and reverse-proxy behavior gets messy
services behave differently depending on where the request started
If your firewall or resolver supports host overrides, use them. It is cleaner than the pile of hosts-file hacks people swear are temporary.
From the lab
IoT isolation without breaking the house
This is the part where good intentions meet Chromecast, printers, cameras, and a smart speaker that becomes emotionally unavailable if multicast traffic changes shape.
IoT isolation works best when you assume deny by default and add only what you can justify.
A typical IoT policy might be:
IoT -> Internet: allow 80/443, DNS, NTP
IoT -> local resolver: allow port 53 to your DNS server
Trusted -> IoT: allow only from devices that manage those endpoints
Home Assistant -> IoT: allow required device ports
IoT -> Servers: block by default
If you use Home Assistant, document every exception. Do not leave yourself mystery rules named allow-stuff-temp-final-2 and pretend that is a system.
Hardware that supports this layout cleanly
You do not need enterprise gear pulled from a rack with its own emotional history.
A few sensible pieces go a long way:
Managed switch: TP-Link TL-SG108E - cheap, small, VLAN-capable, and perfectly adequate for many labs
AirPlay, Chromecast, some printers, and various smart-home devices depend on multicast discovery that does not naturally cross VLAN boundaries.
You can solve this with an mDNS repeater, an mDNS reflector on your router, or by accepting that some devices should stay on the same segment as their controllers. Not every problem needs a heroic design pattern.
2. Backup traffic
A backup job that worked fine on a flat network may suddenly fail because the NAS is now on Servers, the client is on Trusted, and you forgot to allow NFS or SMB.
Be explicit:
NFS - 2049
SMB - 445
rsync - 873
SSH-based backup traffic - 22
3. Reverse proxy reachability
Your proxy may live on Servers while apps sit on Lab, or vice versa. If the proxy cannot initiate to backend services, everything looks dead even though the apps are healthy.
4. Monitoring blind spots
Prometheus, LibreNMS, Zabbix, and friends need access across boundaries. Monitoring is one of the few cases where carefully scoped cross-VLAN access is a feature, not a mistake.
A staged rollout plan that will not ruin your weekend
Do not rebuild the entire network in one night unless you enjoy emergency console sessions.
Phase 1 - Create the VLANs and subnets
create Management, Trusted, Servers, IoT, and Guest
map SSIDs to the right VLANs
move one non-critical device first
Phase 2 - Move infrastructure
move switch and AP management to Management
move the DNS resolver and reverse proxy to Servers
confirm Trusted can still reach core services
Phase 3 - Move IoT and Guest devices
put cameras, TVs, plugs, speakers, and similar devices on IoT
put visitors on Guest
watch logs for unexpected local dependencies
Phase 4 - Add stricter rules
default deny between VLANs
add only documented exceptions
review logs daily for a week
This approach is slower. It is also how you avoid discovering that your spouse's streaming setup depended on a mystery broadcast path you removed in the name of network hygiene.
A default rule philosophy that stays readable
Firewall rules should still be readable six months later by someone who did not memorize every temporary exception. That usually means clear aliases, explicit destination scope, and comments that name the service being allowed.
That means:
group aliases by role, not by random IP memory
comment every allow rule with the actual service need
prefer destination-specific allows over wide-open network access
review rules after major app changes
delete old temporary exceptions aggressively
This is not just security advice. It is maintenance advice.
When you should add more VLANs
Add more segmentation only when you can explain the risk or operational benefit.
Good reasons:
isolated lab experiments
cameras with especially ugly vendor behavior
DMZ-style public services
separate storage or backup replication traffic
Bad reasons:
you saw a neat diagram on Reddit
your switch supports 4094 VLANs and you took that personally
Those are three useful references to keep nearby while wiring up a segmented lab and validating the first policy pass.
Final recommendation
If you are starting from scratch, build five zones and stop there until the network proves you need more. Put management on its own VLAN. Put servers together. Treat IoT like it is guilty until proven innocent. Give guests internet and nothing else.
Most importantly, solve DNS and logging early. People love talking about VLAN IDs. The parts that actually save you are naming, policy clarity, and the ability to see what got blocked.
That is the difference between a segmented network and a confusing one.
Frequently Asked Questions
How many VLANs should a homelab have?
Most homelabs only need 4 to 5 VLANs: management, trusted, servers, IoT, and guest. Add more only when you can explain the risk reduction or operational benefit in one sentence.
Do I need a managed switch for homelab network segmentation?
Yes. If you want proper wired VLAN segmentation, you need a switch that supports 802.1Q tagging. An unmanaged switch will happily forward traffic while pretending your design choices are somebody else's problem.
What usually breaks first after VLAN segmentation?
Usually mDNS-based discovery, local DNS assumptions, backup jobs, or reverse proxy backend access. That is why logging denied traffic during rollout is more useful than guessing.
Should Proxmox management be on its own VLAN?
Yes. Management interfaces should live on a dedicated management VLAN that only trusted admin devices can reach. It keeps the blast radius smaller and the rule set cleaner.
Can IoT devices stay usable after segmentation?
Yes, but you need to allow specific control paths from trusted devices or platforms like Home Assistant. The goal is not to make IoT unusable. The goal is to stop it from roaming the network like it pays rent.
Last verified: 2026-07-31. This article was reviewed against the primary documentation listed below. Unsupported first-person or faux-tested framing was removed unless the claim was backed by a cited primary source.