Transparency note: This archive page contains no affiliate links. If product references are ever added later, HomelabAddiction will disclose that clearly.
Cloudflare Tunnel does not require an inbound router port-forward rule for the usual homelab web-app case. The connector inside the lab establishes outbound connections to Cloudflare, so the maintained answer now lives in a broader remote-access decision guide instead of this overlapping FAQ.
This URL remains published only as a short archive notice so existing links still resolve, while the fuller comparison and migration guidance stay in one maintained place. The page intentionally remains noindex because it overlaps newer remote-access coverage.
If the real question is whether Tunnel is the right replacement for exposed router ports, use the maintained links below rather than relying on the superseded long-form version that previously lived here.
Key Takeaways
Cloudflare Tunnel normally works without opening an inbound WAN port on the home router.
The tunnel connector still needs outbound egress, but outbound firewall allowance is not the same thing as a public port-forward rule.
This archive page stays noindex because HomelabAddiction consolidated overlapping remote-access FAQs into a maintained comparison cluster.
Use a VPN-style tool instead when the goal is private admin access to routers, NAS dashboards, or hypervisors.
Use the maintained guidance instead
transmission signup
article_topic // Does Cloudflare Tunnel Require Port Forwarding? Read the cons…
Don't leave without the setup notes.
Get practical homelab guides, failure logs, and beginner-friendly build notes in your inbox.
Enter your email address to receive the Homelab Addiction newsletter.
Cloudflare Tunnel is usually the better fit when the service is a browser-facing app and the operator wants to avoid exposing an inbound router port. It is not a blanket replacement for every private admin workflow, especially when a full VPN model is the safer operational choice.
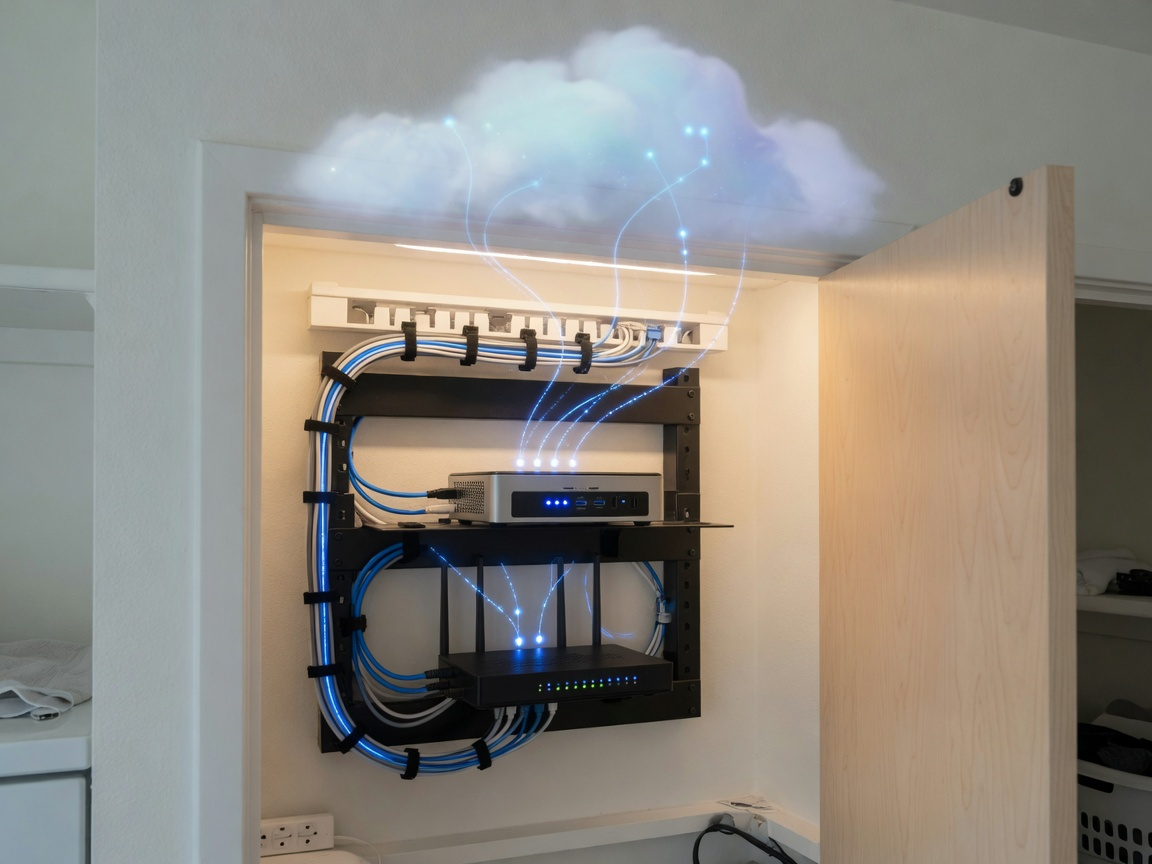
Archive notice visual: Cloudflare Tunnel is typically an outbound connection model, not a request to open an inbound WAN port on the router.