Restic Backup for Homelabs: A 3-2-1 Workflow for Linux Servers, Docker Volumes, and Offsite Copies
Use restic for a practical 3-2-1 homelab backup workflow across Linux servers, Docker volumes, and offsite copies. This refresh focuses on documented repository, retention, and restore-test steps.
FTC disclosure: This article contains affiliate links. If you purchase through these links, HomelabAddiction may earn a commission at no additional cost to you.
Documentation basis: This refresh is based on primary vendor or project documentation. No hands-on testing is claimed unless explicitly stated. Primary sources used in this refresh:
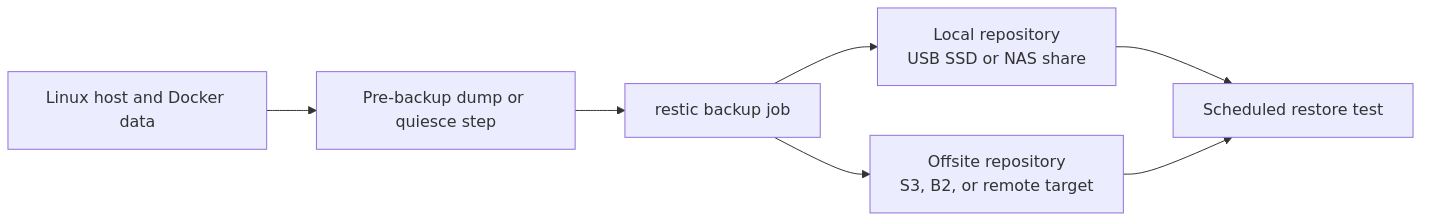
Figure: a simple 3-2-1 restic backup path from Linux and Docker hosts to local storage, offsite copies, and restore checks.
Key Takeaways
restic is a practical fit for homelabs because it combines encryption, deduplicated snapshots, repository checks, and backend flexibility in one small toolchain.
A usable plan still needs more than a backup command: keep a local copy, an offsite copy, and a restore test that runs on a schedule.
Docker backups become safer when you dump or briefly quiesce stateful services before capturing bind mounts or volume data.
Retention is part of the workflow, so forget, prune, and periodic repository checks belong in the runbook.
Backup reporting should land somewhere visible because silent failure is the normal failure mode.
This page helps homelab operators build a recoverable restic workflow for Linux servers and Docker application data by providing a documented 3-2-1 pattern that scales from one host to several.
The refresh is grounded in restic documentation and Docker storage guidance. No hands-on testing is claimed unless explicitly stated on the page.
A practical baseline is to prepare application-consistent data, write snapshots to a local repository, replicate to an offsite target, and schedule restore checks often enough that the runbook stays real.
Why restic Usually Fits Better Than rsync Alone
I still use rsync. It is excellent for fast local copies and migrations. But I do not use rsync alone as my primary backup system anymore.
restic provides snapshot history, deduplication, encryption, repository checks, and backend flexibility without much ceremony. The same workflow can target a USB SSD, an NFS mount, SFTP storage, or Backblaze B2. That matters in a homelab because the storage target tends to change as your setup grows and your budget changes shape.
A common mistake is keeping “backups” as plain mirrored directories on the same NAS. That looks fine until versioning is needed and corruption has already been mirrored too. Very efficient failure, to be fair.
A Backup Architecture That Fits Most Homelabs
A practical layout is simple:
Back up each Linux host to a local or LAN-accessible restic repository.
Keep the repository encrypted with a password file.
Run scheduled backups daily.
Apply retention with forget and prune.
Copy critical datasets offsite to Backblaze B2 or another supported backend.
Test restores on a schedule, not only when panic becomes the project manager.
For small labs, a USB SSD attached to the backup host is fine as the first target. For multi-host labs, use a NAS share or a dedicated backup box. For offsite protection, Backblaze B2 is practical and cheap enough that you do not need a board meeting to justify it.
If you are backing up VMs as well, pair this with Proxmox Backup Strategies: How to Never Lose a VM Again. Restic is excellent for files and application data, but it should complement hypervisor-level backups, not replace them.
Hardware That Fits This Workflow
You do not need to buy your way into a backup strategy, but a few pieces of gear can make operations easier:
I generally avoid backing up Docker's overlay2 filesystem directly. It is large, noisy, and often not what you actually need. The persistent data usually lives in bind mounts or named volumes. Back up the data you can restore with confidence, not the storage internals you hope will somehow make sense later.
Step 4: Handle Docker Data Properly
Here is the thing people get wrong with container backups: a running container is not the problem. Inconsistent writes are the problem.
Static services are easy. Databases are not. If you back up a busy PostgreSQL or MariaDB volume without coordination, you may get a snapshot that exists but is not trustworthy. That is a terrible category of success.
For low-write containers, a brief stop before backup can be the safer path:
I use --group-by host,tags because shared repositories become messy if you do not scope retention properly.
I run check with a subset on the daily job. Full --read-data checks are useful, but not every night unless your repo is tiny and your patience is infinite.
Logging to a file is the minimum. Realistically, ship the result to email, Discord, or your monitoring stack.
Persistent=true is important. If the server is off during the scheduled time, the job runs on next boot instead of pretending nothing happened. Which is nice. Honesty in infrastructure matters because restore day is not the time for surprises.
From the lab
Step 7: Add an Offsite Copy with Backblaze B2
A local backup without an offsite copy is better than nothing. It is not enough if theft, fire, filesystem corruption, or a dramatic power event takes out your primary data and your backup target together.
You can keep the local and offsite repositories separate, which is what I prefer. It keeps restore logic cleaner and lets you apply different retention policies depending on cost and bandwidth.
How I Pick Retention Without Hoarding Everything Forever
Retention is where backup plans quietly become storage problems. The beginner mistake is keeping far too little. The more advanced mistake - which feels very responsible at first - is keeping everything forever until the repository turns into a financial and operational personality test.
My default homelab policy is:
7 daily snapshots
4 weekly snapshots
6 monthly snapshots
1 yearly snapshot
That is enough history to recover from the usual nonsense: a broken update, accidental deletion, silent config damage, or a database mistake you notice next week instead of tonight.
If I have a high-churn dataset, I usually split it into its own repository or at least its own tag. That way a noisy media workflow or camera ingest box does not force the same retention policy onto a low-change config backup.
My rule is simple: every critical service gets a restore drill. For a Docker app, that means I restore its Compose file, data directory, and any database dump into a test path and verify that the structure is actually usable.
The mistake I made: for too long, I treated “restic backup completed successfully” as proof. It only proves a command exited cleanly. A restore test proves you are not lying to yourself.
Common Mistakes I See Repeatedly
1. Backing up live databases without a dump or snapshot plan
This is the classic one. The backup exists. The restore is cursed.
2. Keeping the repository password only on the host being protected
If the host dies and the password file dies with it, you have created encrypted decorative storage. Keep a copy in a password manager and a secure offline note.
3. Ignoring retention until the repository gets huge
Restic will not clean up after you unless you tell it to. Read the official docs for backups and forget/prune policies. They are worth your time.
4. Treating Docker internals as the backup target
Back up the application data, not every transient layer in the engine.
5. Running backups with no alerting
At minimum, check systemctl status restic-backup.service and journalctl -u restic-backup.service. Better yet, wire failures into your normal monitoring path.
What to Learn Next
Once this is running reliably, I would expand in this order:
Add backup metrics or alerting.
Separate high-churn and low-churn datasets into different retention policies.
Add hypervisor-aware backups for VMs and NAS-native snapshots where appropriate.
Run a full restore drill quarterly.
That is how you get from “I have backups” to “I can survive a bad day without rebuilding my life from screenshots.”
FAQ
Is restic good for Docker backups?
Yes, if you back up the right data. Restic is excellent for bind mounts, named volumes, and exported database dumps. It is not magic - you still need consistency for stateful apps.
Should I use one repository for every host?
For most homelabs, separate repositories per host or per major role are easier to manage. Shared repositories can work, but you need careful tagging and retention scoping.
Is Backblaze B2 required?
No. Any backend restic supports can work. I like B2 because it is simple, affordable, and common in homelab circles, but SFTP, local disks, and NAS targets are all viable.
How often should I run restic check?
I like a lightweight subset check on daily jobs and a fuller integrity check on a slower schedule, such as weekly or monthly, depending on repository size.
Can I restore just one file instead of the whole backup?
Yes. That is one of restic's best features. You can list snapshots, inspect contents, and restore a single file or directory without pulling back the entire dataset.
Final Recommendation
If you want one backup tool that works across Linux servers, Docker hosts, and offsite object storage without demanding an enterprise-sized attention span, restic is the one I recommend most often.
Set it up once. Script it properly. Test restores on purpose. Then go do something more interesting with your homelab than wondering whether your backups are imaginary.
transmission signupstatus: open channel
article_topic // Restic Backup for Homelabs
Start building a smarter homelab.
Join readers learning Proxmox, networking, storage, backups, and self-hosting without breaking everything.
Enter your email address to receive the Homelab Addiction newsletter.
Beginner-friendly
No gatekeeping. Just clear, actionable guides.
1 useful email / week
Practical tips, real-world setups, and lessons learned.
Zero hype, practical only
What works, what breaks, and how to fix it.
Reply to any email with what you're building. I read and reply to as many as I can.
— The Homelab Addiction Operator
support // the lab
Found this guide useful?
If it saved you time or a rebuild, you can support more practical homelab guides.